INDEPENDENT THINKING. ENTERPRISE EXPERIENCE.

Cloud architecture.Built for thereal world.

I’m Manuel, an Azure Solutions Architect. I turn complex infrastructure into secure, well-built environments that people can depend on.

Based in San José, Costa Rica. Working across borders.
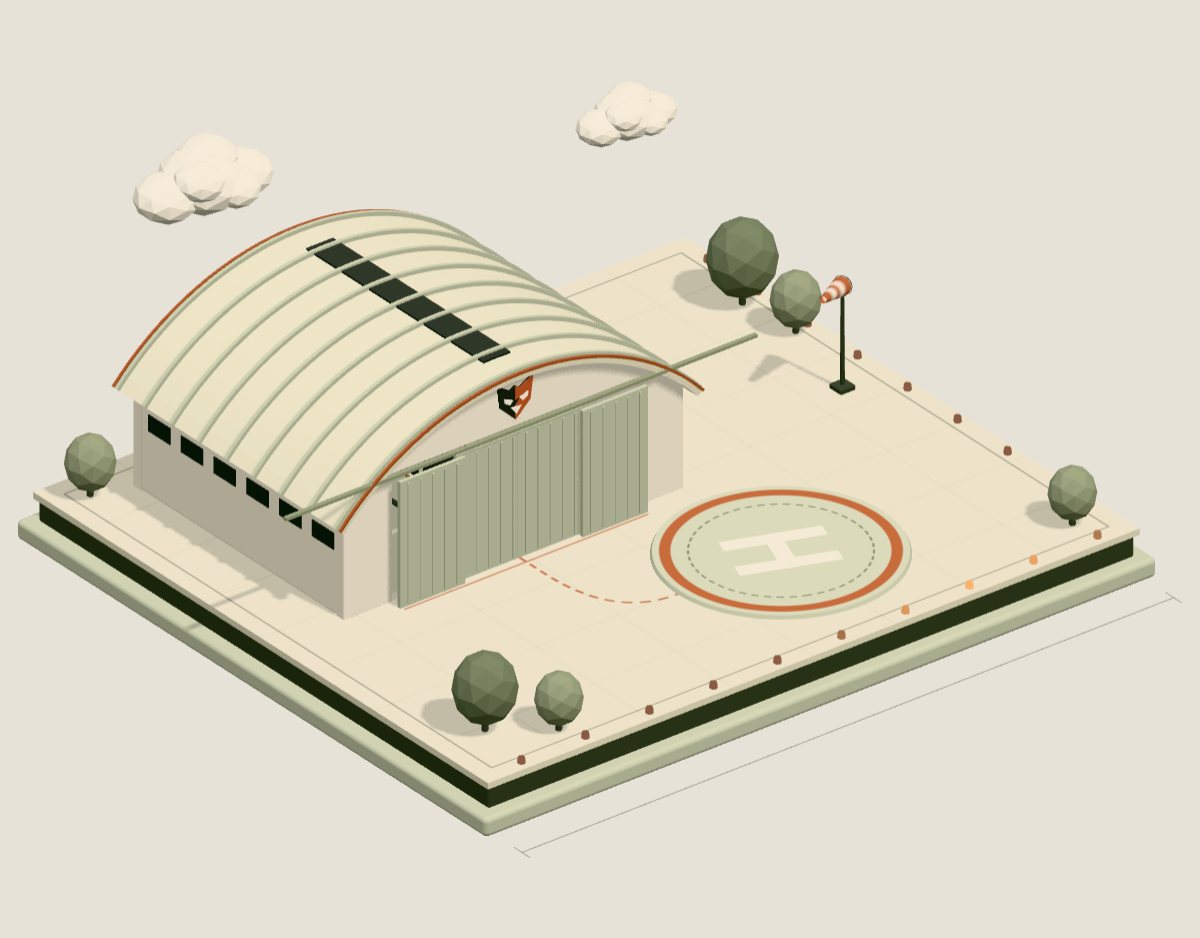
FIG. 01 — THE HANGAR
Scale model of the Wolfskycloud hangar and its helicopter landing pad. 01 HANGAR 02 LANDING ZONE 03 WIND
Every flight starts from a solid landing zone.AZURE / M365

Enterprise scale.
Personal accountability.

10K+devices managed
8K+users supported
16sites in one Azure migration

01 / SELECTED WORK

The work behind
the architecture.

Real environments. Tangible outcomes.
A selection of engagements, with client details anonymised.

02ENDPOINT MODERNISATION / GLOBAL ASSESSMENT10,500 devices. Under six months.650 test centres

Led a Windows 10 1607 to 22H2 upgrade across 10,500+ devices, roughly 650 test centres, and four regional subdomains. Delivered in under six months against previous vendor estimates of more than a year.

SCCMWindowsGlobal delivery
03MICROSOFT 365 / WORKSPACE MIGRATIONA new workspace for 3,000+ people.300+ SharePoint sites

A tenant-wide move from Google Workspace to Microsoft 365 using BitTitan. Migrated mail and Drive data to Exchange Online and OneDrive, and designed and provisioned more than 300 SharePoint sites.

BitTitanOneDriveSharePoint
04IDENTITY & SECURITY / ZERO TRUSTSecurity, built in from day one.6 phases completed
05IDENTITY & ENDPOINT / POLICY-AS-CODEA repeatable baseline for every tenant.11 access policies

Designed and delivered a Conditional Access baseline of 11 policies, including break-glass and exclusion patterns, plus an Intune security group structure that became a repeatable starting point for subsequent deployments.

Entra IDIntuneConditional Access

02 / EXPERTISE

From the
first diagram
to day two.

I work across the Microsoft stack, connecting architecture decisions to the detail that makes them work in production.

Let’s discuss your environment
01

Azure foundations

Landing zones, hub-and-spoke networks, Firewall Premium, governance and monitoring. Built with Bicep and designed to grow.

02

Identity & security

Entra ID, Conditional Access, Defender and Zero Trust controls. Clear policies, practical protection, repeatable deployment.

03

Migrations & modern workplaces

Multi-site infrastructure moves, Microsoft 365 migrations, tenant consolidation and Azure Virtual Desktop.

04

Endpoints at scale

Intune and SCCM co-management, Windows upgrade campaigns, Autopilot and modern provisioning across thousands of devices.

05

Automation & observability

PowerShell, Azure Automation, KQL and Log Analytics. Tools that make operations more visible and less manual.

06

Architecture & advisory

Well-Architected reviews, M365 licensing strategy, CSP structures and technical pre-sales, grounded in delivery experience.

03 / THE LAB

Always building.

Proofs of concept, reusable tools, and ideas
tested against real engineering problems.

01ALZ-Bicep Hub & SpokeBicep

Modular Azure Landing Zone implementation using Bicep with hub-and-spoke topology, Azure Firewall Premium, and centralized logging.

Bicep / Infrastructure / Azure
02Conditional Access Policy EnginePowerShell

Policy-as-code framework for deploying and testing Conditional Access policies at scale with built-in validation and compliance checks.

PowerShell / Microsoft Graph / Identity
03Intune Baseline DeploymentPowerShell

Repeatable Intune configuration baseline covering compliance policies, device configuration profiles, and app protection policies.

PowerShell / Intune / Endpoint
04Azure Monitor Analytics WorkbooksKQL

KQL-based analytics dashboards for Azure security posture, Defender for Endpoint threat intelligence, and operational metrics.

KQL / Azure Monitor / Analytics
05Multi-Tenant M365 ProvisioningPowerShell

Automated tenant provisioning and configuration orchestration across multiple M365 environments with tenant-switching utilities.

PowerShell / M365 / Automation
06M365 Baseline SecurityPowerShell

Enterprise-grade security baseline with 6 phases: Identity & Access (PIM, Conditional Access), Email Protection (Defender for Office 365), Endpoint Security (Intune + EDR), Data Governance (DLP, sensitivity labels), and Compliance Audit. Full Zero Trust implementation with policy-as-code.

PowerShell / M365 / SecurityExplore the implementation
07AVD on Azure Verified ModulesBicep

Near-full Azure Virtual Desktop environment composed from vendored Azure Verified Modules, with a monthly automated sync pipeline for upstream module versions and session hosts joined to an existing AD DS domain, deployed via Azure DevOps.

Bicep / Azure Verified Modules / AVD
08Application Integration NetworkBicep

Dedicated Azure virtual network carrying two application paths: a Function App to SQL Managed Instance over TCP 1433, and API Management to an on-premises IIS backend over TCP 443. Peered into three existing production networks and deployed through approval-gated Azure DevOps pipelines.

Bicep / Networking / Azure DevOps

A CLOSER LOOK / AUTOMATION

Less repetition.
More engineering.

I use AI-assisted workflows to develop and validate scripts, policies, and runbooks. The useful part is what follows: consistent deployments, clearer reporting, and more time for the work that needs judgment.

ENDPOINT PERFORMANCE PIPELINES
4,000+

EPA devices covered by automated telemetry collection and performance reporting.

CollectValidateReport

04 / BEHIND THE WORK

Manuel Arce
SAN JOSÉ, COSTA RICA / WORKING ON MOUNTAIN TIME

Manuel Arce.
Architect. Engineer.

I like understanding how things fit together.
Then making them work better.

I’m a Microsoft Certified Azure Solutions Architect Expert, delivering Azure and Microsoft 365 engagements for North American MSP and CSP partners.

Previously, I worked as a Customer Success Architect across LATAM and North America at Microsoft, contracted through Persistent Systems, and went on to lead a regional team of 9–12 architects.

Today, my work combines hands-on engineering with that broader perspective: the architecture, the implementation, and the people who will operate it.

CERTIFICATIONS & CREDENTIALS

  • Azure Solutions Architect ExpertMicrosoft Certified
  • Azure Network Engineer AssociateMicrosoft Certified · AZ-700
  • Microsoft Certified TrainerMCT
  • ISO 27001 Internal AuditorInformation security
  • Azure Virtual DesktopAVD
When a project needs a larger team

I work with a senior network of Microsoft-experienced engineers, several ex-Microsoft, with active certifications across Azure, M365 security, Intune and Entra ID. The team scales to the engagement.

HAVE SOMETHING IN MIND?

Let’s build
something solid.

A project, a tricky migration, or a fresh perspective.
Let’s start with a 30-minute conversation.